
Arsenal Forge
Alert enrichment that brings MITRE ATT&CK and CISA context to analysts through MCP and retrieval-augmented generation.
BLodgic was built around a simple idea: organizations should not have to choose between senior cybersecurity expertise and the ability to execute.
BLodgic combines senior cybersecurity practitioners, hands-on engineering, and purpose-built technology to help organizations govern AI, strengthen security programs, navigate compliance, and turn risk into executable action.
Our work draws on experience inside some of the most demanding security environments in banking, technology, research and higher education. That experience shapes how we work. We give clear advice, we stay for the implementation, and we measure success by risk reduced rather than pages delivered.
Along the way we saw experienced professionals spending too much time matching evidence and policy language by hand. So we built Audit CADDIE, our AI-powered GRC and compliance platform, to remove that friction while keeping people accountable for judgment.
Recommendations come from experience building and operating security programs.
Automate low-value work without automating accountability.
Recommendations should be defensible to executives, regulators, auditors and technical teams.
A report is not the objective. Reducing risk is.
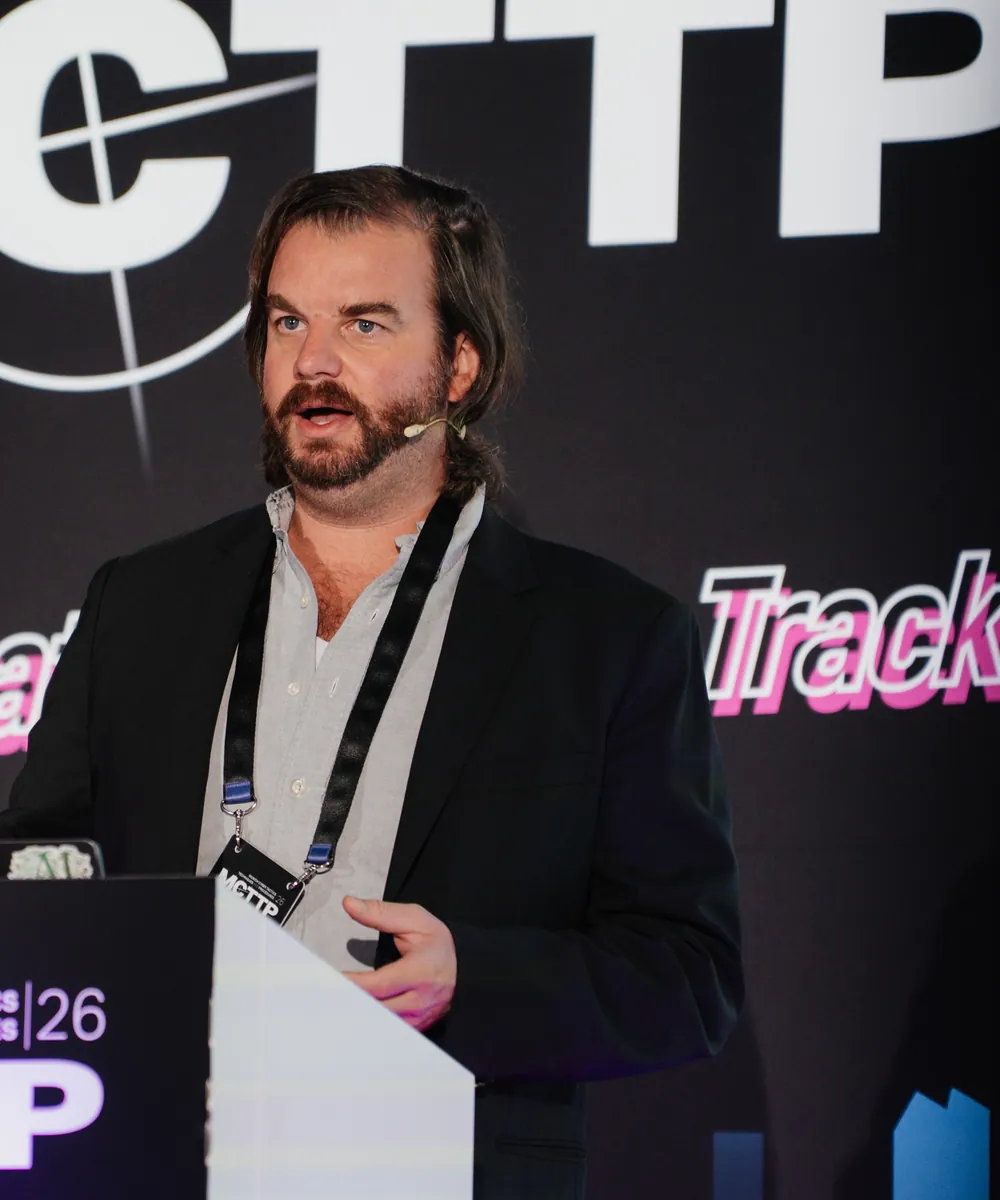
Brennan is a cybersecurity, AI and data science leader with nearly two decades of experience across financial services, technology, security operations and regulated environments, with roles associated with JPMorgan Chase, the Federal Reserve Bank of New York, Bloomberg, Goldman Sachs and HSBC.
Audit CADDIE is a separate software product owned by BLodgic. It automates evidence analysis, control mapping and compliance workflow.
BLodgic is the experienced pilot. Our practitioners use the platform where it helps, and remain accountable for interpretation, recommendations and execution.
Alert enrichment that brings MITRE ATT&CK and CISA context to analysts through MCP and retrieval-augmented generation.
Threat models, abuse cases and control patterns for retrieval-augmented generation in enterprise environments.
Practical guidance on Model Context Protocol servers, tool permissions and connector risk, including the LinkedIn Learning course on MCP use cases.
Tell us where you are stuck. We will help determine whether you need strategy, hands-on execution, specialized expertise, Audit CADDIE, or a combination.